What to Look for When Hiring a Managed Service Provider (MSP): The Complete Business Guide
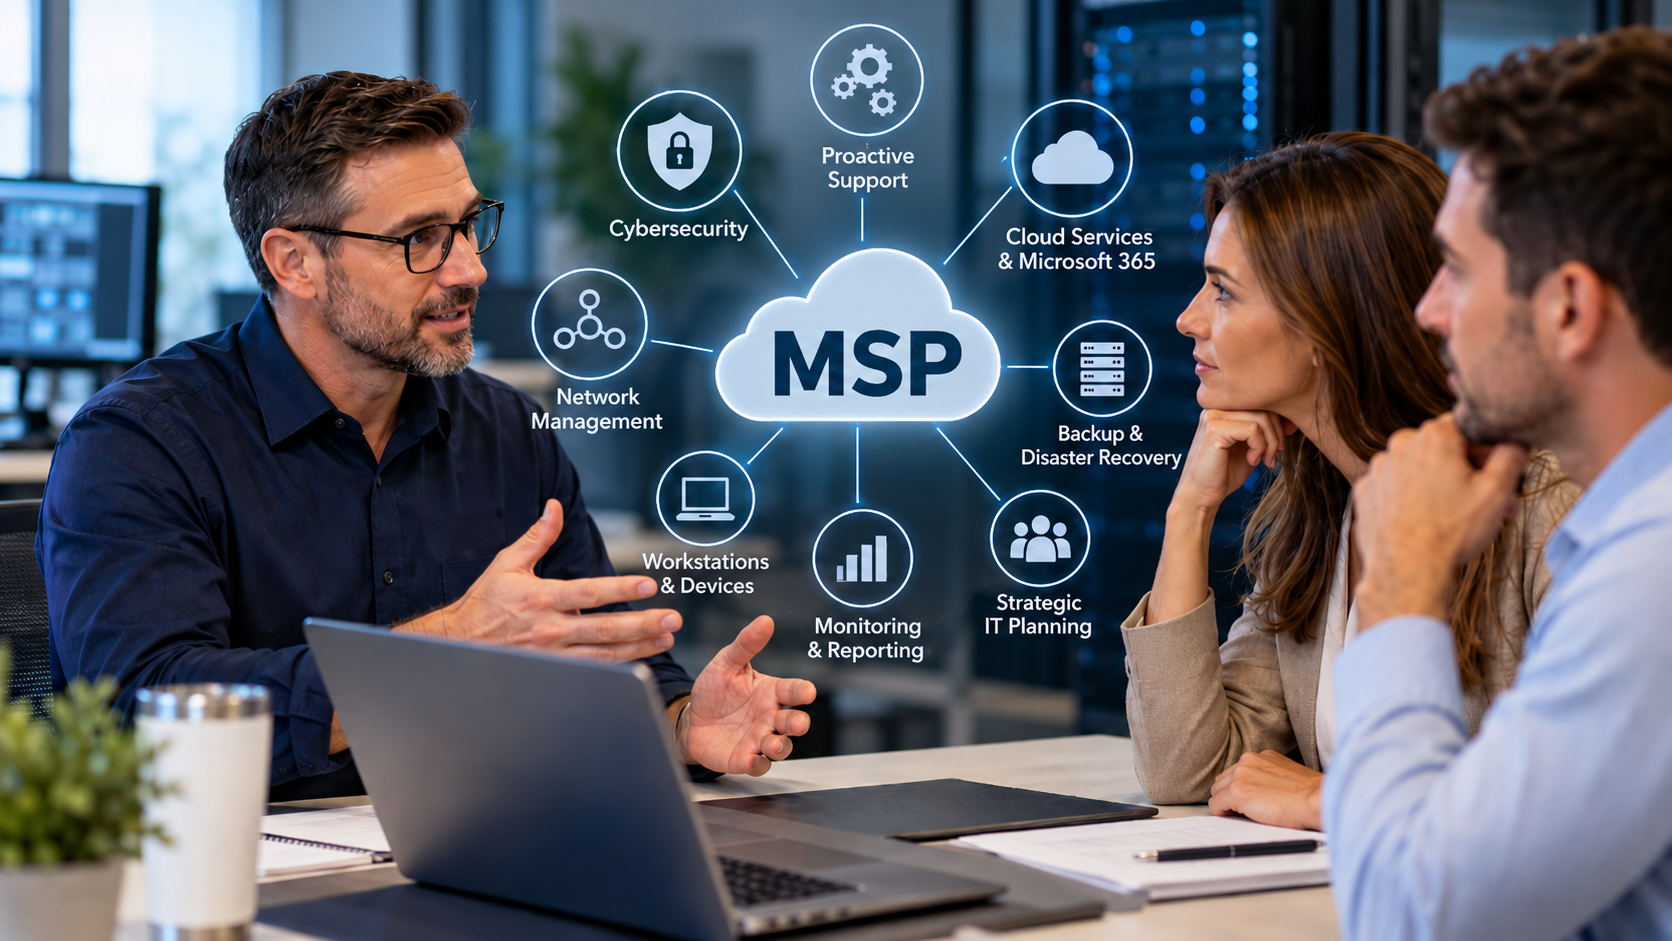
Choosing a Managed Service Provider (MSP) is not simply a matter of finding someone to fix computers when they break. The provider may be responsible for your network, servers, cybersecurity, Microsoft 365 environment, backups, business applications, employee accounts, and the technology your organization relies on every day.
A well-managed MSP can reduce disruption, strengthen security, create predictable costs, and help your organization make better technology decisions. A poorly matched provider can introduce security risks, leave issues unresolved, create unexpected expenses, or make it unnecessarily difficult to regain control of your own systems.
The challenge is that two MSPs can advertise nearly identical services while offering very different levels of coverage, competence, responsiveness, and accountability. Before hiring an MSP, evaluate what it supports, how it operates, what it costs, how performance is measured, and what happens if the relationship ends.
This guide brings together operational, technical, financial, and contractual considerations, with questions you can use during interviews and proposal reviews.
1. Define Your IT Environment and Business Requirements
Before comparing providers, create a practical inventory of what must be supported. Start with users and devices, then work outward to infrastructure, applications, and business processes.
- Employees and endpoints: desktops, laptops, remote employees, contractors, smartphones, tablets, and shared devices.
- Servers and core services: physical and virtual servers, Active Directory, DNS, DHCP, SQL databases, file shares, IIS, and print servers.
- Network infrastructure: firewalls, switches, wireless access points, VPNs, multiple offices, internet connections, and site-to-site links.
- Cloud and collaboration: Microsoft 365, Exchange Online, Teams, SharePoint, OneDrive, Entra ID, Azure, or other services.
- Business applications: accounting software such as QuickBooks, customer or project systems, proprietary applications, and vendor-hosted platforms.
- Security and recovery: endpoint protection, email filtering, vulnerability management, backups, disaster recovery, and cybersecurity monitoring.
- User services: onboarding, offboarding, workstation provisioning, printers, scanning to network folders, and telephone or conferencing systems where relevant.
Identify which systems are business-critical, what downtime costs, which users require priority attention, and what support is already performed internally. An environment with 20 office workers using cloud applications may need something very different from a 20-person company operating custom servers and remote field laptops.
Request a scope-of-services and responsibility matrix from each prospective MSP. It should state which assets and tasks are included, which are excluded, who owns each function, and which services involve separate charges. Do not rely on the phrase “we handle everything.”
2. Investigate the MSP’s Experience, Reputation, and Staffing
An MSP’s size or sales presentation does not establish its ability to support your business. Look for practical experience, stable staffing, sound internal processes, and customers with needs comparable to yours.
Questions to ask include:
- How long have you operated, and what types of businesses do you normally support?
- How many employees, service-desk technicians, system administrators, engineers, and security specialists do you have?
- Will our account be assigned a primary team or account manager?
- Do you outsource helpdesk, monitoring, after-hours coverage, security operations, or field services? If so, to whom?
- How do you cover vacations, illness, employee turnover, and unusually high ticket volume?
- Can we meet the people who will actually support us and review their relevant experience?
- Are you equipped to scale with us as employee counts, sites, and requirements grow?
Certifications from Microsoft, Cisco, CompTIA, Fortinet, or other vendors can indicate training, but they are not substitutes for real troubleshooting ability, reliable processes, and customer service skills. Ask about staff development, documentation practices, and how difficult cases are handled.
Speak with client references
Request references from organizations of similar size and complexity, ideally ones that have experienced both routine support and a significant incident. Ask whether the MSP meets its commitments, is proactive, respects budgets, communicates clearly, fixes recurring issues, and takes responsibility when something goes wrong. A reference’s experience during an outage is often more informative than its experience during the sales process.
3. Customer Service, Accessibility, and Professionalism
Employees interact with the MSP through the helpdesk, so everyday service quality matters just as much as sophisticated technical capabilities.
Determine the normal support hours, supported time zones, holiday coverage, ways to contact the service desk, and whether customers can speak directly to a technician. Confirm whether after-hours service is a staffed function, an on-call rotation, or emergency-only coverage. 24/7 automated monitoring does not necessarily mean 24/7 live support.
Ask whether onsite service is available, where technicians are located, how onsite dispatch is prioritized, and whether travel time is billable. Observe the provider’s communications during the evaluation itself. Does it listen, answer directly, explain technical concepts without condescension, and follow up when promised?
Also establish how management-level concerns are handled. A designated account manager is useful, but businesses should have a route to senior service leadership or an executive when a serious problem cannot be resolved through normal channels.
Executive and VIP support
Some businesses require priority white-glove support for executives, conference rooms, or time-sensitive meetings. If a CEO is accustomed to having an IT technician begin work within 10 to 15 minutes, ask whether the new MSP can contractually meet that specific target, during which hours, and under what conditions. Clarify whether VIP service includes onsite assistance, meeting preparation, travel support, or an assigned engineer. Do not assume that a general “high priority” ticket offers the same protection.
4. Service Level Agreements: Response, Restoration, and Resolution
A Service Level Agreement (SLA) should define measurable service commitments, not simply promise “fast support.” At minimum, discuss priority levels, acknowledgment, active technical engagement, escalation, customer updates, restoration targets, and reporting.
Response time is the time until the action defined as a response occurs. That may be an acknowledgment, a call from a technician, or actual troubleshooting. Resolution time concerns fixing the issue; restoration time concerns getting the affected service usable again, potentially through a workaround. These are different measurements and should not be confused.
| Priority | Illustrative incident | Example initial response target |
|---|---|---|
| P1: Critical | Company-wide outage, major security incident, essential service unavailable | 15 minutes, 24/7 if contracted |
| P2: High | Department unable to work, critical application impaired | 1 hour during agreed coverage |
| P3: Medium | One user has a significant problem with a workaround available | 4 business hours |
| P4: Low | Routine request, minor issue, or software question | 1 business day |
These are example negotiation targets, not universal industry standards. The contract must define its own priority criteria, service hours, exclusions, and clock rules.
Ask how priorities are determined and who can change them. Does the SLA clock pause while awaiting a vendor or customer response? How often will the business receive updates on critical incidents? What happens if the MSP repeatedly misses targets? Can you see reports showing actual performance rather than averages selected for a sales presentation?
Be cautious of blanket uptime guarantees such as “99.999% network availability” unless the provider defines the systems being measured, the calculation, the exclusions, and which underlying services it actually controls. An MSP cannot independently guarantee the availability of every third-party platform or internet connection.
5. Helpdesk Ticketing, Escalation, and Incident Ownership
A mature MSP operates a consistent ticket-management process. Every request should be logged with the affected user or system, business impact, priority, assigned owner, troubleshooting history, communication, vendor interactions, and resolution.
Ask for an overview of the ticket lifecycle. Can employees use phone, email, and a portal? Are tickets assigned automatically or reviewed by a coordinator? Who monitors aging tickets? Can customers reopen tickets that were closed prematurely? Are repeat problems analyzed for a common cause?
Support teams may be organized into Level 1, Level 2, specialized engineering, and vendor escalation. The exact titles matter less than whether responsibility transfers cleanly. When an incident moves between technicians, the next person should have the full history, accept ownership, and continue communicating. Users should not repeatedly explain the same problem because internal notes or handoffs are inadequate.
Supporting unfamiliar products and third-party services
An important question is what happens when the MSP receives a call about an application its technician has never used. A professional response is to collect relevant information, check documentation, research safely, involve a qualified teammate or vendor, and keep the customer informed. It should not be to guess at a fix, abandon the ticket, or immediately blame another company.
Ask whether the MSP coordinates with an ISP, software vendor, cloud provider, telephone carrier, printer manufacturer, or another third party when an incident spans multiple services. Its responsibility to coordinate should be clearly defined, even if it cannot directly repair the third-party product.
6. Technical Coverage: Endpoints, Servers, Applications, and Networks
Have the provider review your actual environment and identify any unsupported technologies before a contract is signed.
Workstations and remote computers
Confirm support for Windows and macOS, hardware failures, software installation, operating system problems, remote access, VPN connections, device replacement, and users who are away from the office for months. Ask whether printers, scanners, peripherals, and common “how do I” requests are covered.
Servers and business infrastructure
Where applicable, confirm competence with Active Directory Domain Services, Group Policy, DNS, DHCP, Windows Server, Linux, SQL Server, IIS, file and print services, virtualization, storage, and server capacity planning. Distinguish monitoring a server from fully administering its operating system, applications, permissions, and recovery.
Business applications
List accounting, ERP, CRM, industry-specific, and internally developed programs. An MSP may not be the software developer, but it should be able to maintain operating-system dependencies, permissions, network connectivity, and installation requirements, and coordinate with the application vendor. Document precisely what is covered.
Network infrastructure
Determine whether the MSP supports your existing firewall, VPN, switches, and wireless access points, including products such as SonicWall or other brands already installed. If existing equipment is obsolete, out of vendor support, or cannot be secured, ask for a supported transition plan and the reason for any recommended replacement. The need to standardize an MSP’s preferred technology stack should not, by itself, justify unnecessary purchases.
For network monitoring, ask about device availability, interface errors, bandwidth usage, internet connectivity, latency, packet loss, wireless health, VPN status, firmware, configuration backups, and alert thresholds. Distinguish routine availability monitoring from security log analysis or a staffed security operations center.
7. Cybersecurity: Evaluate Both Your Protection and the MSP’s Own Security
An MSP with administrative access to business systems creates a significant third-party security relationship. General IT support, managed security services, and 24/7 threat detection are not automatically the same offering.
Discuss coverage for MFA, identity management, endpoint detection and response (EDR), antivirus, network hardening, firewall management, vulnerability scanning, remediation, email protection, privileged access, logging, security awareness training, and incident response. Ask which items are included in the monthly price and which require separate software licenses or a specialist Managed Security Service Provider (MSSP).
Equally important, ask how the MSP protects its own remote monitoring and management (RMM) tools, administrative credentials, documentation, and access to customer environments. Questions should include:
- Is MFA required for technicians and administrators, preferably phishing-resistant MFA for high-risk accounts?
- Are individual, least-privilege administrative identities used instead of broadly shared credentials?
- Are privileged activities logged, reviewed, and time-limited when practical?
- How are passwords, API keys, and recovery secrets stored?
- Are separate customer environments appropriately isolated?
- How are subcontractors vetted, and how is access removed when a technician leaves?
- What is the notification process if the MSP itself experiences a security incident?
- Can the provider share a meaningful independent assessment, SOC 2 report, or other evidence relevant to the actual services supplied?
Frameworks such as the NIST Cybersecurity Framework 2.0 supply-chain guidance and the CIS Critical Security Controls provide useful references. A certification or report should be evaluated for scope and findings, not treated as an unconditional guarantee.
8. Email Security, Phishing, and Microsoft Exchange Administration
Email protection should cover more than an ordinary spam filter. Ask about phishing and malware filtering, attachment and link inspection, impersonation detection, SPF, DKIM, DMARC, quarantine review, compromised-account response, and user reporting procedures.
If your company uses Microsoft Defender for Office 365, Barracuda, or another security product, determine whether the MSP can support the existing configuration or proposes a replacement. Request a demonstration of the process for employees to report a suspicious message and how the helpdesk investigates a possible phishing campaign affecting multiple mailboxes.
Some organizations maintain custom Exchange Online mail flow rules, such as warning banners for external messages or messages that appear to impersonate employees. Confirm that the provider can review, manage, test, and document such rules without breaking normal mail delivery.
9. Patch Management and Change Control
Your MSP should be able to explain exactly how it manages updates to workstations, servers, applications, firewalls, switches, and other infrastructure. Automatic patching is useful, but indiscriminate changes can interrupt critical business applications.
Look for patch assessment, risk-based prioritization, pilot testing, deployment schedules, restart coordination, exceptions, rollback plans, failed-update reporting, and urgent security remediation. Ask how the MSP proves that devices have actually received patches, including laptops that are rarely connected to the office.
Formal change management
Major changes such as firewall updates, authentication-policy modifications, switch replacements, and cloud migrations should have a documented request, risk assessment, approval, implementation window, communication plan, rollback steps, and post-change validation. Emergency changes may follow an expedited process but still require a record and subsequent review. Ask how affected staff and the MSP’s own support teams are notified of changes.
10. Backup Strategy and Verifiable Data Recovery
Backups should be designed around actual recovery requirements, not simply around a product the MSP happens to resell. Inventory server data, databases, file shares, critical endpoints, Microsoft 365 mail and calendars, SharePoint, OneDrive, and any other applications where data loss would disrupt operations.
The familiar 3-2-1 backup principle provides a useful starting point: three copies of important data, two different storage media or systems where practical, and at least one offsite copy. Depending on the risks, consider additional immutable, offline, or isolated recovery copies so an attacker who compromises production systems cannot also destroy every backup.
Ask whether the MSP supports your existing backup software, such as Veeam, and whether it offers onsite and geographically separate offsite copies. The right architecture depends on requirements, not on a one-size-fits-all rule that every device must have exactly the same backup arrangement.
Two recovery metrics that must be defined
- Recovery Point Objective (RPO): the maximum acceptable age of recovered data, or how much recent data the business can afford to lose.
- Recovery Time Objective (RTO): the target amount of time to restore a service to an acceptable level after disruption.
A four-hour RPO and a four-hour RTO measure different things. Recovery objectives should be defined per system, with the business understanding their cost implications.
Prove that backups can be restored
Require scheduled, documented test restores. A green backup status report does not demonstrate that a SQL database, virtual machine, Exchange mailbox, or complete server will actually recover. Verify individual-file recovery, application integrity, whole-system recovery where appropriate, and the time required. Ask who pays for emergency restores and testing.
Microsoft 365 backup specifics
Microsoft 365 offers built-in resiliency and retention features, and Microsoft also sells Microsoft 365 Backup for supported workloads. Do not assume those mechanisms cover all data types, all Teams content, third-party apps, or every desired retention period. Require a written list of protected workloads, restore options, location of protected data, costs, and retention rules. Microsoft 365 Backup overview.
11. Disaster Recovery, Business Continuity, and Incident Response
A backup policy is not a complete disaster recovery plan. A serious incident can affect people, communications, facilities, identity systems, internet access, or an entire cloud environment.
The MSP should help develop a written recovery plan identifying critical services, system dependencies, RTO and RPO targets, emergency contacts, responsibilities, restoration order, alternate operating methods, vendor contacts, and communication procedures. It should be accessible to authorized people even when the normal network is unavailable.
Business continuity addresses how the company keeps operating during disruption.
Disaster recovery focuses on restoring affected technology.
Incident response addresses detecting, containing, investigating, and learning from security events. All three should be coordinated but are not interchangeable.
Ask who leads a major incident, whether the MSP offers forensic or ransomware response services, which specialists are called when necessary, and how evidence is preserved. Require periodic tabletop exercises and meaningful recovery testing, not a plan that is written once and forgotten.
12. Microsoft 365, Cloud Administration, and License Ownership
Many MSPs act as Microsoft Cloud Solution Providers (CSPs), purchasing and managing subscriptions on behalf of customers. This can simplify administration, but license commitments must be understood separately from the MSP’s support contract.
Confirm support for Exchange Online, Teams, SharePoint, OneDrive, Microsoft Entra ID (formerly Azure AD), Intune, Defender, Conditional Access, Single Sign-On, and any other Microsoft 365 components the company uses.
Questions to ask:
- Can we buy licenses through you, directly from Microsoft, or from another authorized reseller?
- Are prices itemized by product, term, and user count?
- Who monitors unused licenses and upcoming renewals?
- How do monthly and annual subscriptions differ in flexibility and cost?
- Can licenses be transferred if we change MSPs, and what cooperation is required?
- Which subscriptions remain financially committed even if our MSP agreement ends?
Microsoft New Commerce Experience terms can restrict cancellation or seat reductions after a short cancellation window. Transfers between CSP partners are possible under specified procedures, but are not automatic. Review Microsoft’s cancellation policy and CSP transfer guidance.
Your business should retain control of its Microsoft 365 tenant, domains, data, and independently secured emergency access.
An MSP should use appropriately scoped delegated administrative access, such as Microsoft Granular Delegated Admin Privileges (GDAP) where applicable, rather than insisting on sole permanent control.
13. Remote Work, BYOD, and Mobile Device Management
Employees who work remotely, travel for long periods, or use personal devices create additional support and security requirements.
Ask whether the MSP can manage devices that rarely connect to the office network, enforce configuration policies, troubleshoot over secure remote channels, and deliver replacement equipment to the field.
Bring Your Own Device (BYOD) requires an explicit policy addressing what the company can manage, what personal information administrators can access, and how business information is protected or removed.
Microsoft Intune and other Mobile Device Management (MDM) or Mobile Application Management (MAM) solutions may help separate company data from personal device use.
Include smartphones, tablets, lost devices, remote wipe capabilities, and the process for revoking access when employment ends. Verify whether these services are included in the MSP fee or require per-device licenses and extra support charges.
14. Employee Onboarding, Offboarding, and Computer Deployment
New employee onboarding can involve Active Directory or Entra account creation, Microsoft 365 licenses, MFA enrollment, email, group permissions, Single Sign-On, shared files, application access, workstation provisioning, printers, and communications tools. Agree on required notice, standard turnaround times, urgent exceptions, and who authorizes access.
If your organization expects complete standard onboarding within three business hours, ask whether the MSP can meet that target, what prerequisites apply, and whether it will be included in the SLA.
Offboarding should include promptly disabling accounts, revoking sessions and VPN access as appropriate, reclaiming devices, managing email and business data, removing licenses, and recording completion. Time-sensitive terminations need a faster route than an ordinary low-priority ticket.
Purchasing, staging, and delivering equipment
Clarify whether the MSP researches hardware, obtains quotations, orders computers, installs software, configures security, enrolls devices into management, ships directly to employees, and provides onsite installation. Ask whether you can supply your own computer for the MSP to configure and return, what the shipping address and risks are, and what turnaround time is realistic.
Confirm whether hardware markups, staging fees, delivery, travel, warranty work, and device disposal are additional expenses.
15. Documentation, Asset Inventory, and Access to Your Own Systems
Good documentation allows the next technician to continue work without starting from the beginning. It also protects the customer from becoming dependent on one employee or one provider.
Ask for regularly maintained inventories of physical and virtual assets, owners, locations, serial numbers, warranties, software versions, IP addresses, network devices, licenses, and renewal dates.
Request documentation of network topology, VLANs, firewall rules, VPNs, DNS and DHCP, Group Policy, servers, backup procedures, application dependencies, vendor contacts, and recovery instructions.
The customer should have an agreed right to current documentation and essential access information. That does not mean passwords should be emailed or distributed in plain text.
Use secure vaults, controlled access, audit logs, independent business-owned accounts, and emergency-access procedures.
Clarify when documentation is updated, who can view it, how it is exported, and how the MSP will provide it during a transition or termination.
16. Proactive Maintenance, Reporting, and Strategic Planning
A provider should not exist solely to react to incidents. It should regularly review system health, recurring ticket causes, security posture, backup failures, patch compliance, hardware lifecycle, licensing, and capacity.
Require practical reports covering open and resolved tickets, SLA attainment, response and resolution trends, recurring incidents, network and device health, unresolved vulnerabilities, backup results, and the status of recommended actions. Ask for sample reports before signing.
For long-term planning, some MSPs offer an assigned account manager or Virtual Chief Information Officer (vCIO). Quarterly or periodic technology reviews can cover business growth, upcoming projects, hardware replacement, cybersecurity improvements, licensing costs, and budget forecasts. The purpose is not simply to sell additional products.
The MSP should explain why a recommendation matters and how success will be evaluated.
Administrative time and small projects
Ask whether the agreement includes a monthly block of administrative or engineering time for tasks such as Active Directory audits, new Group Policies, application testing, security reviews, or documentation improvements. Establish whether these hours expire, roll over, require prior approval, or apply only to certain technicians. This can materially change the value of two otherwise similar proposals.
17. Transitioning From an Existing MSP
Replacing an IT provider requires careful coordination. The incoming provider should perform discovery before making sweeping changes and should present a written handover plan.
The plan should cover initial assessments, inventory, knowledge transfer, administrative access, domain registrar and DNS control, Microsoft 365 partner relationships, licensing, firewall and VPN credentials, backup validation, vendor contracts, RMM removal and installation, security agents, documentation, and user communication.
Ask what downtime is expected, which changes will occur after hours, how backups will be checked before cutover, who coordinates with the outgoing MSP, and how problems will be resolved during a stabilization period.
The incoming provider should identify unsupported equipment and urgent risks, but should distinguish true remediation needs from optional technology standardization.
Confirm who pays for discovery, onboarding, project work, and any overlapping period of support.
18. MSP Pricing Models and 2026 Industry Benchmarks
Pricing is one of the most important parts of the MSP decision. A low advertised rate can become expensive once servers, security, backups, onsite support, licensing, and project work are added. Conversely, a higher all-inclusive price may represent good value when it genuinely replaces many separately purchased services.
Common pricing models
- Per user: one monthly charge for each supported employee, sometimes covering multiple devices and applications.
- Per device: separate monthly charges for workstations, servers, network hardware, and other assets.
- Tiered packages: basic, standard, and premium plans with different support and security coverage.
- Flat-rate or all-inclusive: a negotiated monthly price for a clearly defined environment and scope.
- Co-managed IT: services added alongside an internal IT team, with responsibilities divided in writing.
- Hourly or prepaid blocks: break/fix or planned support paid as used, often with weaker cost predictability and less proactive coverage.
Published U.S. pricing benchmarks
The following are approximate 2026 planning ranges.
Note: Survey findings, advertised entry prices, and provider quotations use different scopes, so they should not be treated as directly interchangeable.
| Service or pricing unit | Approximate 2026 U.S. range | Important qualification |
|---|---|---|
| Helpdesk-focused services | $35 to $100 per user/month | May omit substantial infrastructure or security work |
| Co-managed IT | $50 to $120 per user/month | Depends on what internal IT retains |
| Fully managed IT | $100 to $250 per user/month | Broader or compliance-heavy plans may exceed $300 |
| Workstation or laptop management | $50 to $125 per device/month | Sometimes already covered by per-user pricing |
| Physical server management | $100 to $400 per server/month | Complex or high-availability servers may cost more |
| Managed firewall | $30 to $75 per device/month | Subscription licensing and replacement hardware may be extra |
| Managed network switch | $15 to $40 per device/month | Depends on scope and network size |
| Managed security/MDR add-on | $10 to $60 per user or endpoint/month | Distinguish EDR software from staffed 24/7 security response |
| Hourly support or engineering | Roughly $125 to $250+ per hour | Depends on expertise, geography, and time of day |
| Separately contracted vCIO advisory | Roughly $1,500 to $5,000/month | Some plans include periodic advisory meetings |
According to a 2026 survey by Best IT MSP, fully managed IT services cost an average of $145 per user per month, with most providers charging between $110 and $185.
Co-managed IT services, where an MSP works alongside a company’s existing IT staff, average $85 per user per month.
Separately, MSP Signal found that advertised entry-level plans have a median price of approximately $75 per user per month. However, these lower-priced plans may include fewer services.
When comparing MSP pricing, always consider which services are included, not just the monthly price.
Sources: 2026 MSP Pricing Benchmark
MSP Signal public-price analysis
DataStrive, managed IT pricing context
2026 per-device estimates.
Backup, licensing, and other add-on costs
Not all add-ons have meaningful standardized rates. A server backup service depends on storage, retention, recovery objectives, and the protected applications.
Microsoft 365 third-party backup might be charged per user, per workload, or by data volume.
For one concrete example, Microsoft 365 Backup lists a consumption price of $0.15 per GB per month of protected content. That is a product charge, not the full price of MSP management, restore testing, or additional support.
Other commonly separate charges include onboarding, network projects, security remediation, workstation staging, physical installation, after-hours labor, emergency dispatch, migrations, hardware, cloud consumption, third-party licensing, and extended data retention.
Do not automatically add every benchmark to a per-user managed IT quote. Ask for an itemized schedule showing which capabilities are already included and which are additional.
19. Special Offers, Discounts, and What Can Be Negotiated
The first price offered is not necessarily the final arrangement.
Depending on provider and contract term, organizations may be offered a free initial IT assessment, an invoice and contract review, waived setup charges, a discounted first month, one free month of service, a trial period, annual prepayment discounts, volume discounts, bundled security services, or included engineering hours.
As an actual published example, Exigent has advertised one free month of qualifying managed services, waived onboarding charges, and a six-month penalty-free cancellation guarantee with certain annual agreements. Such promotions have eligibility requirements and can change.
Review the current published offer and fine print rather than assuming it is universally available.
Discounts may also be negotiable for nonprofits, multiple locations, large user counts, standardized equipment, or agreements with predictable scope.
Some providers may offer discounted Microsoft licensing or bundled backup and security products.
Negotiate value and protections, not just price.
Useful concessions may include priority executive support, a certain number of onsite visits, regular disaster recovery tests, quarterly security reviews, included administrative hours, capped annual increases, written response guarantees, and fair exit assistance.
Before accepting a promotion, ask whether it requires a multi-year commitment, auto-renewal, minimum seat count, or separate licensing agreement. A free month rarely justifies unfavorable cancellation or service terms.
20. Build a Realistic IT Budget and Compare Total Cost
The monthly MSP invoice is only one part of the budget. Separate recurring operations from one-time onboarding, equipment refresh, planned projects, and contingency funding.
Budget categories should include:
- Managed support, maintenance, and monitoring.
- Microsoft 365 and other software licenses.
- Cloud infrastructure and usage-based charges.
- Backup storage, disaster recovery, and test restores.
- Security products, specialist response, training, and compliance work.
- Computer, server, firewall, switch, and wireless replacement schedules.
- Projects, migrations, installations, and office moves.
- Extra support, travel, emergency labor, and contingency funding.
Worked example: 25-employee company
Assume a hypothetical 25-user organization with two servers, one firewall, and Microsoft 365 Business Premium. The following is an illustrative model, not a quotation.
The model deliberately assumes that the base MSP package does not include the separately listed servers, firewall, or backup services.
| Monthly expense | Calculation | Estimate |
|---|---|---|
| Fully managed IT | 25 users at $150 | $3,750 |
| Server management | 2 servers at $250 | $500 |
| Firewall management | 1 firewall at $50 | $50 |
| Microsoft 365 Business Premium | 25 users at $22 | $550 |
| Microsoft 365 backup | 25 users at assumed $8 | $200 |
| Server backup services | 2 servers at assumed $150 | $300 |
| Recurring monthly total | $5,350 |
The $22 per-user Microsoft 365 Business Premium line reflects a published U.S. annual-commitment list price at the time of writing; payment frequency, tax, available plans, and reseller terms may affect the actual bill. The backup rates are scenario assumptions, not universal prices.
(See Microsoft’s official business pricing.)
| First-year budget component | Illustrative amount |
|---|---|
| Recurring IT and licensing, 12 months | $64,200 |
| Initial onboarding and transition | $2,500 |
| Planned project allowance | $5,000 |
| Subtotal | $71,700 |
| Illustrative contingency of 10% | $7,170 |
| First-year planning total | $78,870 |
The 10% reserve is simply a modeling choice and may be inadequate for a business with aging infrastructure or major transformation projects. Hardware purchases, ISP charges, telecom services, taxes, and other excluded items would have to be added where applicable.
Compare three-year cost, not just the first invoice
Ask each prospective MSP to provide a common-format 12-month and 36-month total cost estimate using the same inventory and required scope. Include onboarding, setup, licenses, annual increases, equipment purchases, optional services, projects, and termination costs. A provider offering $110 per user might cost more than a provider offering $170 once equivalent security, backup, onsite support, and engineering are included.
A sound IT budget should also track user-count changes, unused licenses, aging hardware, planned maintenance, and risk reduction. The goal is predictable spending and measurable business value, not simply the lowest monthly rate.
21. Managed Services Contracts, Exclusions, and Financial Transparency
An MSP agreement commonly consists of a Managed Services Agreement (MSA), a Service Level Agreement (SLA), and sometimes one or more Statements of Work (SOWs) for projects. Some providers combine these documents. The important issue is whether their terms are clear and consistent.
Review:
- Services and covered assets, including users, servers, locations, and applications.
- Normal and emergency coverage hours, contact methods, response targets, and escalation.
- Fees, billing schedule, minimum charges, rate cards, travel, and pass-through license costs.
- Support exclusions, project pricing, and the approval process for additional charges.
- Agreement start date, duration, automatic renewal, and notice deadlines.
- Price increases, user-count changes, and minimum commitments.
- Third-party products and whether licenses survive the support contract.
- Confidentiality, data protection, subcontractors, and notification duties.
- Liability limitations, service credits, insurance, disputes, and governing law.
- Project change orders, acceptance criteria, and who owns resulting deliverables.
- Suspension terms, termination rights, transition duties, and data return.
“All-inclusive” is not a contractual definition. Ask explicitly whether onsite visits, after-hours calls, new-user setup, workstation provisioning, network upgrades, device moves, backup restores, vendor coordination, and major incident recovery are covered.
Likewise, do not insist that every technical incident can have a guaranteed fixed completion time. Software defects and complex vendor failures can make exact completion dates impossible. For well-defined projects, written scope, deliverables, estimated timeline, milestones, price structure, and change-control requirements are reasonable. For incident response, measurable engagement, restoration targets where feasible, communications, and escalation are more meaningful.
Require detailed invoices, authorization before unbudgeted work, and an agreed process for disputing charges. Have qualified legal counsel review substantial agreements, especially long-term commitments and liability limitations.
22. Insurance, Compliance, and Third-Party Risk
When hiring a Managed Service Provider (MSP), it is important to understand what protections are in place if something goes wrong.
Your MSP may have access to sensitive company information, customer records, financial systems, and critical business infrastructure. If the provider makes a serious mistake, experiences a security breach, or causes an extended outage, your business could suffer financial losses.
Before signing an agreement, make sure the provider has appropriate insurance and understands any legal or industry-specific requirements that apply to your organization.
What Insurance Should an MSP Have?
Just like other businesses, an MSP should carry insurance to protect itself and its customers against certain risks.
There are several types of insurance worth asking about:
-
General Liability Insurance: Typically covers certain claims involving physical injuries or property damage. For example, if an MSP technician accidentally damages equipment or causes an injury while working at your office, this insurance may provide coverage.
-
Technology Errors and Omissions (E&O) Insurance: Helps protect against certain claims involving professional mistakes, negligence, or failure to properly deliver contracted technology services. For example, if a technician incorrectly configures a system and causes a major business disruption, this insurance may cover some resulting claims.
-
Cyber Liability Insurance: Provides protection for certain expenses and liabilities arising from cybersecurity incidents, such as data breaches or ransomware attacks. Depending on the policy, coverage may include investigations, data recovery expenses, legal costs, and notifications to affected individuals.
-
Workers’ Compensation Insurance: Provides benefits to employees who experience work-related injuries or illnesses, as required by applicable law. For example, if an MSP technician is injured while installing equipment at your office, workers’ compensation may cover eligible medical expenses and lost wages.
Ask the MSP to provide proof of its insurance, commonly called a Certificate of Insurance (COI), along with information about its coverage limits.
Keep in mind that having insurance does not automatically mean every type of damage or financial loss will be covered. Insurance policies have exclusions, limitations, and specific conditions.
You should also review the MSP’s contract to understand how much responsibility the provider accepts if its actions cause damage to your business.
What Does Compliance Mean?
Depending on your industry, your business may be required to follow specific laws, regulations, or security standards for handling and protecting information.
This is commonly referred to as compliance.
For example:
-
HIPAA: Applies to certain healthcare organizations and their business associates. It establishes requirements for protecting patients’ health information.
-
PCI DSS: A security standard applicable to organizations that store, process, or transmit payment card information, as well as certain service providers. Its purpose is to help protect credit and debit card data.
-
FTC Safeguards Rule: Requires certain financial institutions, such as some lenders, finance companies, and other covered businesses, to maintain appropriate safeguards for customer information.
-
Privacy Laws: Depending on where your business operates and whose information it handles, privacy laws may establish requirements concerning the collection, storage, sharing, and protection of personal information.
-
Government Contract Requirements: Companies working with government agencies may be required to follow additional cybersecurity standards or contractual security requirements.
Not every business is subject to every regulation.
However, if your organization must comply with specific requirements, you should make sure the MSP understands them and can support your compliance efforts.
For example, a healthcare organization handling protected patient information may need its MSP to sign a Business Associate Agreement (BAA). This is a legal agreement that establishes certain responsibilities for protecting health information.
Who Is Responsible if Something Goes Wrong?
One important point to understand is that hiring an MSP does not automatically transfer your company’s legal or regulatory responsibilities to the provider.
For example, if your company is legally required to protect certain customer information, you generally cannot avoid that responsibility simply because an outside IT company manages your systems.
The MSP may be responsible for performing specific security tasks under its contract, but your business may still be accountable for ensuring the applicable requirements are met.
This is why it is important to clearly document which responsibilities belong to the MSP and which remain with your organization.
Ask whether the MSP can help with security assessments, audits, documentation, access reviews, and reports that demonstrate your company is meeting its obligations.
What Is Third-Party Risk?
Third-party risk refers to potential problems that may arise when your business relies on outside companies for important services.
Your MSP is considered a third-party service provider because it is an outside organization supporting your business.
However, the MSP may also rely on other companies to deliver its services.
For example, it might use:
-
An outside company for after-hours helpdesk support.
-
A separate cybersecurity company to monitor threats.
-
A cloud provider to store your backups.
-
Third-party software for remote computer management.
-
Subcontractors to perform onsite technical work.
This is not necessarily a problem. Many MSPs use specialized outside providers to deliver reliable services.
The important consideration is understanding who has access to your systems and information, what those companies are responsible for, and how their activities are secured.
Ask whether the MSP uses subcontractors or outside service providers, what access they receive, and whether they follow the same security and confidentiality requirements.
You should also understand who is responsible if one of those companies causes a problem.
Questions to Ask the MSP
-
What types of business insurance do you carry, and what are the coverage limits?
-
Can you provide proof of insurance?
-
What happens if one of your technicians accidentally damages our systems or causes data loss?
-
Does your contract limit your financial responsibility if your company makes a mistake?
-
Do you have experience supporting businesses with our industry’s security or compliance requirements?
-
Can you assist with security audits, compliance documentation, and technical assessments?
-
What procedures do you follow if our company’s information is exposed or stolen?
-
How quickly will you notify us if you discover a security incident affecting our systems or data?
-
Do you use subcontractors or outside companies to provide any of your services?
-
How do you ensure those outside companies follow appropriate security practices?
-
Will you provide documentation showing what security measures are in place and how they are maintained?
Why This Matters
Most businesses hire an MSP because they want reliable technical support and someone they can trust to manage important systems.
However, even experienced providers can make mistakes, and no company is completely immune to cybersecurity incidents.
The goal is not to find an MSP that promises nothing will ever go wrong. Such a promise would be unrealistic.
Instead, look for a provider that takes reasonable precautions, carries appropriate insurance, understands its responsibilities, and has established procedures for addressing problems when they occur.
A reputable MSP should be transparent about these matters and willing to explain how it protects both its own business and yours.
23. Ownership, Exit Strategy, and Avoiding Vendor Lock-In
Plan for the end of the relationship before it begins. A business should not become unable to operate or change providers because one MSP has sole possession of administrative access, documentation, domains, backup data, or essential subscriptions.
Clarify who owns domains and registrar accounts, Microsoft 365 tenants, cloud subscriptions, licenses, hardware, backups, technical documents, configuration files, custom scripts, and security logs. Some provider-supplied tools are legitimately licensed only during the agreement, but that must be disclosed.
The contract should specify how the MSP will provide documentation and exports, transfer eligible licenses, help an incoming provider, return owned equipment, remove its agents, revoke access, and securely handle retained data. Ask about handover assistance fees, data retrieval deadlines, and any charge for restoring or exporting backups after termination.
An MSP can reasonably charge for defined transition services, but it should not withhold company-owned systems or essential information to pressure a customer into renewing.
24. Warning Signs to Watch For
Warning signs do not always disqualify a provider, but patterns of evasiveness deserve investigation:
- No written SLA or refusal to explain what “response” means.
- Vague pricing, undefined exclusions, or frequent unexpected invoices.
- A refusal to show sample reporting or explain its ticket process.
- Repeated ticket handoffs without ownership or history.
- Backup claims unsupported by actual restore testing.
- Weak MFA, shared privileged credentials, or poorly secured RMM access.
- Inability to explain critical-incident escalation or third-party coordination.
- No credible plan for disaster recovery or major staffing disruptions.
- Pressure to replace working equipment without a technical justification.
- No current network, asset, or configuration documentation.
- Unclear licensing ownership or resistance to customer administrative control.
- Promises of flawless security, universal uptime, or impossible resolution guarantees.
- Excessive commitment periods combined with weak termination protections.
- Unwillingness to explain how the business will move to another MSP.
Also watch for a consistently reactive service culture where recurring problems are repeatedly patched without root-cause investigation or prevention.
25. Questions to Ask Prospective Managed Service Providers
Use the same questionnaire for each finalist. Record answers in writing and ask for supporting documentation where important.
Business and staffing
- How long have you been in business, and what is your client retention rate?
- How many technicians and engineers do you have, and what roles will support our account?
- Which support functions are outsourced or provided by subcontractors?
- Can we speak with comparable client references and meet our likely support team?
- How do you handle staffing gaps, business growth, and escalation to senior leadership?
Customer support and service levels
- What are normal, weekend, holiday, and emergency coverage hours?
- Can employees call directly, and what types of requests are excluded?
- What do your SLA priorities, response targets, restoration targets, and missed-target remedies mean?
- How are tickets logged, assigned, escalated, handed over, and closed?
- Can you provide executive or VIP support with a specific response target?
- What is your onsite service area and cost, including after-hours dispatch?
Technical operations and security
- Will you support our existing computers, servers, firewall, switches, wireless equipment, and VPN?
- How do you handle industry-specific applications and third-party vendors?
- What do you monitor, how are alerts handled, and what reports will we receive?
- How do you manage updates, firmware, testing, changes, rollback, and unpatched devices?
- What cybersecurity technologies are included, and what requires a separate MSSP or MDR service?
- How do you secure your own administrative accounts, remote access, RMM tools, and customer environments?
- What is your phishing-reporting, investigation, and compromised-account process?
Backups, cloud, and user services
- Which servers, endpoints, Microsoft 365 workloads, and applications are backed up?
- Where are backups stored, how are they protected, and when are test restores performed?
- What RPO and RTO commitments can you support, and will you help maintain a disaster recovery plan?
- Can we retain our Microsoft 365 tenant, domain, licensing flexibility, and independent emergency administrative access?
- Do you support BYOD, remote field laptops, smartphone management, and employee privacy requirements?
- What are standard and urgent onboarding and offboarding turnaround times?
- Do you procure, configure, ship, install, and warranty-support equipment we or you purchase?
- What documentation, asset tracking, administrative work, and strategic planning are included?
Pricing, contract, and exit
- What is the complete monthly price for our actual inventory and required scope?
- What are your per-user, per-device, server, onsite, after-hours, project, and emergency rates?
- Are onboarding, backup, cybersecurity, software licenses, and administration included or additional?
- Do you offer waived onboarding, trials, discounts, included engineering time, or fixed-price projects?
- How do seat-count changes, renewals, annual price increases, and third-party commitments work?
- Will you provide itemized invoices and 12-month and 36-month total cost projections?
- What is the handover plan, expected downtime, and transition cost from our present MSP?
- What are our cancellation rights and possible termination costs?
- How will you return documentation, company data, access, backups, and assets when we leave?
26. Score and Compare Proposals Consistently
Build a simple evaluation scorecard before choosing. The example below is designed for a typical business and can be adjusted if cybersecurity, uptime, or special applications are especially critical.
| Evaluation category | Suggested weighting |
|---|---|
| Technical capabilities and scope | 20% |
| Service quality, ticket process, and SLA | 20% |
| Security, backup, and disaster recovery | 20% |
| Documentation and strategic planning | 15% |
| Pricing, budgeting, and contract transparency | 15% |
| Staffing, reputation, and client references | 10% |
| Total | 100% |
Give each provider the same requirements and scoring scale. Ask for sample SLAs, reports, transition plans, and a complete price schedule. Some deficiencies should be treated as mandatory pass/fail criteria: for example, the inability to protect administrative access, verify backups, or return essential customer-owned information should not be offset by an attractive monthly price.
Choose a Partner, Not Just a Helpdesk
The best MSP is not automatically the largest company, the lowest bidder, or the one with the longest service list. It is a provider that understands the business, supports the technologies actually in use, communicates reliably, secures its privileged access, maintains usable documentation, and takes appropriate responsibility for resolving problems.
Evaluate the total financial relationship as carefully as the technical services. Compare the full 12-month and 36-month costs, confirm what is included and excluded, negotiate reasonable safeguards, and keep control over essential business systems and data.
A strong provider should help the organization become more resilient, secure, efficient, and prepared for change, while making it straightforward to measure service quality and retain flexibility if the relationship no longer meets your needs.
Further Reading and Sources
The historical interview questions and earlier IT-provider material used to develop this guide were supplemented with contemporary vendor guidance and published 2026 pricing research.
- 2026 MSP Pricing Benchmark, published survey
- MSP Signal, publicly advertised MSP pricing
- DataStrive, managed IT pricing guide
- ITADON, managed IT and per-device pricing examples
- Exigent, example of an MSP introductory offer
- Microsoft 365, official U.S. business plan pricing
- Microsoft 365 Backup, official price model
- NIST, Cybersecurity Framework 2.0 supply-chain risk guide